The checklist, in the order to do it.
- Secure the email address the account is registered to — its own password, its own second factor.
- Set an exchange password that exists nowhere else.
- Enrol a real second factor (authenticator app, passkey or hardware key) and put its backup codes somewhere that survives losing the phone.
- Take your phone number off the login and recovery path.
- Set an anti-phishing code.
- Switch every security alert on, with app notifications as a second channel.
- Confirm the API key list is empty.
- Turn on the withdrawal whitelist, and its waiting period for new addresses, which on Binance is a separate switch.
Item one is not a setting inside the exchange, and that is why it gets skipped.
A typical takeover breaks no cryptography. Somebody gets in through a reused password or a convincing message, and then finds that once inside, there is nothing in the way. No allowlist. No waiting period. Notifications going to an inbox the attacker also controls.
So the useful question is not "how do I make my account secure". It is three separate questions, and they have different answers: what stops someone getting in, what limits what they can do once they are in, and what tells me it happened. The eight settings below are grouped that way, because that is the order in which they earn their keep.
Why the order matters more than the list
You will find the same eight items on a hundred other pages. The lists are not wrong. What they usually miss is that these settings interact, and doing them in the wrong sequence creates an afternoon of annoyance that ends with someone switching a protection back off.
Two examples. If you enable a withdrawal allowlist before you have a second factor properly working, you will need that second factor to add your first address — and if the authenticator is half set up, you are now locked out of your own withdrawals. And if you change the password last, after configuring everything else, every session you were relying on gets invalidated at the worst moment.
Do the login protections first. After that the order is less fussy, with one exception: leave the whitelist until last, because its waiting period and later changes to the list can pause withdrawals, and you want everything else settled before that clock starts.
Group one: settings that stop someone logging in
1. The email address the account is registered to
It matters more than anything inside the exchange, because whoever owns the email owns the recovery path. Give it a password used nowhere else and its own second factor, and keep it off anything public.
2. A password that exists in exactly one place
Not a strong password. A unique one. Length and symbols matter far less than the fact that the string has never been typed into any other site. Credential-stuffing works because people reuse; an attacker with a list from an unrelated breach simply tries the pairs against exchanges until one opens.
In practice this means a password manager, because nobody remembers fifteen unique strings and the ones who claim they do are using a pattern that a script can guess. If you are not going to use a manager, at minimum make the exchange password and the email password different from each other and from everything else. Those two are the pair that matters.
3. A second factor that is not a text message, with its backup codes off the phone
An authenticator app generates a six-digit code from a shared secret on your device. A passkey signs a challenge with a key that lives in your phone's secure hardware or your password manager. A hardware security key does the same thing on a separate physical device. All three resist remote attacks in a way that a text message does not, because none of them can be redirected by convincing a mobile operator to move your number.
Set one of these up before anything else in this section, because several other settings will ask you to confirm with it. Binance's own help centre documents both its in-house authenticator app and passkeys as options, and the related-articles list on that page in September 2026 was almost entirely passkey material, which tells you where they are pushing people.
Which one to pick is a genuine decision rather than a ranking. The comparison is here, but the short answer is that an authenticator app is the most portable and the passkey is the most convenient, and having both is not overkill.
Enrolment usually hands you backup codes or a setup key. Save them in the same sitting, somewhere that is not the phone you just enrolled, because they decide whether a lost phone costs you an afternoon or a month. Where they hold up and where they do not is a short read.
4. Take the phone number off the login and recovery path
This one feels like a downgrade, which is why it gets left undone. If your account can be recovered, or logged into, or have its withdrawal settings changed using only a code sent to your phone number, then your account's real security is whatever your mobile operator's retail staff will do for a stranger with a plausible story.
You often cannot remove the number entirely — some exchanges require one, and it is genuinely useful for alerts. What you can usually do is stop it being an accepted verification method once a stronger one exists, and separately, put a port-out lock or transfer PIN on the number with your operator. That second step happens outside the exchange and takes one phone call. The mechanics of a SIM swap are worth reading once so that the call to your operator is specific.
If you only do one thing from this group, make it the email address in step one. Everything else on this page can be reset by whoever reads that inbox.
Group two: settings that stop money leaving if someone gets in
5. The withdrawal whitelist, plus its waiting period
A whitelist — some exchanges call it an allowlist, or address management — means withdrawals can only go to addresses you have registered in advance. On its own that is useful but incomplete, because someone who is already inside your account can add their own address. The part that makes it work is a delay on newly added addresses.
Binance's withdrawal settings page, read in September 2026 and again on 3 October 2026, splits this into two switches. The whitelist restricts withdrawals to listed addresses. A separate setting, the Whitelist Withdrawal Limit, suspends withdrawals to newly added addresses for 24, 48 or 72 hours, whichever you choose. Switching the whitelist off while the limit is on suspends withdrawals for that period too. Turn both on: the list without the limit has no delay at all. That window is the actual protection. It converts a silent theft into something you have a day or more to notice and stop.
A day is a long time in somebody else's plan.
The same page documents a one-step withdrawal option, which lets small amounts go to an already-listed address without completing two-factor verification each time. That is a convenience feature and it is honest about being one. I leave it off. The saving is a few seconds; the cost is that a session someone else has hijacked can move money without meeting a second check.
There is a real trade-off here and it is not small. The full argument is in its own piece, but the compressed version: if you move funds out rarely and to the same few places, turn it on and pick the longest waiting period you can live with. If you move funds to new destinations weekly, the allowlist will make you miserable and you will end up disabling it at the worst possible moment.
6. API keys: create none, and check none exist
An API key is a credential that lets software act on your account. Most people never need one. The relevant setting for most readers is not "configure API keys carefully" — it is "open the API management page, confirm the list is empty, and leave".
If you do need a key, the permissions are granular and the important one is withdrawal. A key with trading permission can lose you money through bad trades; a key with withdrawal permission can lose you the balance outright. Restrict by IP address if the tool supports it. The permission model is broken down here.
Group three: alerts that tell you someone got in
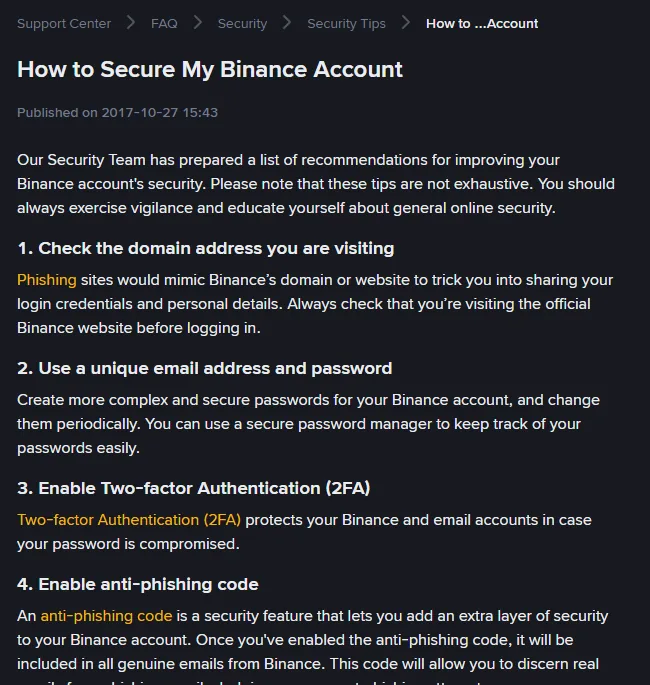
7. An anti-phishing code
This is a short string you choose, which the exchange then puts in its genuine messages; Binance's page says all its genuine emails and texts carry it once it is set. A message with the wrong code should not be trusted, and one without any code is reason enough not to act on it. It is a small, narrow, extremely cheap protection and it takes about ninety seconds.
The rules are specific enough to be worth knowing before you sit down: Binance's help page on the feature, which the page itself showed as updated on 28 August 2026, requires a code of six to eight characters, using at least three of the four character types — uppercase letters, lowercase letters, digits and underscores — and rejects other special characters. Pick something you will recognise instantly and would never type into a form.
What it does not do: it does not protect you from a fake website, a phone call, or a message on a social platform, because none of those are emails from the exchange. The limits are worth understanding before you start treating the presence of the code as proof of anything.
8. Every notification switched on, going somewhere you read
Login alerts, withdrawal alerts, device alerts, settings-change alerts. Turn all of them on even though some are noisy. The entire value of detection is that the alert arrives while you can still do something.
One detail people get wrong: if the alerts go only to the email address that is also the account's recovery address, then an attacker who has taken that email can read and delete the warnings before you see them. Where the exchange lets you add push notifications on the mobile app as well, do it. Two channels, one of which is not email.
While you are in that part of the settings, find the login history. Every serious exchange keeps a record of sessions, devices and recent account activity. Find that page now, while nothing is wrong, so that you know what a normal week looks like. Reading it for the first time during an incident, with adrenaline up, is how people mistake their own old tablet for an intruder. How to read the record takes ten minutes and is worth doing once.
Which settings matter most against bulk, phishing and targeted attacks
It is worth being explicit about the three kinds of attention an ordinary account gets, because the settings above are not equally useful against all of them, and knowing which one you are defending against stops you over-investing in the wrong place.
The bulk attack is a script working through credentials from an unrelated breach. It does not know who you are and will not try twice. A unique password and any second factor makes you invisible to it, which is why those two come first and why they are enough for a great many people.
The opportunistic attack is a phishing message sent to a list you are on, or a fake advertisement above a search result. It is aimed at a category rather than at you. What defeats it is either a phishing-resistant second factor, which refuses to work on the wrong domain, or the habit of never reaching your account through a link. Notice that both of those are about the login, not about the account settings.
The targeted attack is somebody who knows you specifically hold crypto — because of something you said publicly, a group you are in, or a leak from a service you used. This is where the withdrawal controls earn their inconvenience, because a targeted attacker is prepared to spend time and will often get past the login eventually. The delay on newly added addresses is the only protection on the list that keeps working after the login has been lost, for as long as it stays switched on, which is why the alert for a settings change matters as much as the delay.
Most readers are only in the first two categories, and should not lose sleep about the third. But the third is the one that produces the stories. The boring settings at the bottom of the account's security page matter more than the ones the interface shows you first.
Two security settings people switch on and then regret
I said there were two. Here they are, and I want to be fair to both, because in the right hands each is a good idea.
A hardware security key as the only second factor. A physical key is the strongest widely available option. It is also a small object that can be left in a hotel, put through a wash cycle, or lost in a move. People who register exactly one key and no backup method eventually find out what the account recovery process feels like. That process is not quick. Register two keys, or a key plus an authenticator app. One key alone is a single point of failure that you paid for.
Aggressive withdrawal locks on an account you actually trade from. A 72-hour hold on every new address is excellent for a long-term holding account. On an account you use to move funds around weekly, it produces a predictable pattern: three months of friction, then one urgent evening where the delay is intolerable, then the feature comes off and never goes back on. Match the setting to how you really use the account, not to how you would like to be the kind of person who uses it.
There is a cleaner solution to both problems, which is to stop asking one account to do two jobs. A holding account with severe locks and no API access, and a separate working account with a small float and lighter settings (on a platform that offers them, a sub-account under the same identity, not a second personal account), gives you the protection where the money is and the convenience where the activity is.
How long setup takes: doing it in one sitting
If you want to work straight through, the sequence below is what I would follow. It assumes a brand new account with no balance, which is the easiest case and the reason this guide argues for doing it before the first deposit.
| Step | What you do | Roughly |
|---|---|---|
| 1 | Secure the email account first: unique password, its own second factor | 5 min |
| 2 | Set the exchange password from a manager, not from memory | 2 min |
| 3 | Enrol an authenticator app or passkey; write down the backup codes and put them somewhere off the phone | 8 min |
| 4 | Remove the phone number as an accepted verification method (the operator PIN can wait for a phone call later) | 2 min |
| 5 | Set the anti-phishing code | 2 min |
| 6 | Turn on every alert, add push as a second channel | 2 min |
| 7 | Check the API key list is empty | 1 min |
| 8 | Enable the withdrawal whitelist, then switch on its waiting period for new addresses (a separate setting) | 3 min |
The backup codes in step three quietly decide how this ends. Codes stored as a screenshot in your phone's photo library are backed up by the same account that your authenticator recovery might depend on, which is not a backup at all. Where to put them instead is a short read and it saves the worst version of this story.
If you have not opened an account yet and you would rather see the whole thing in sequence on one exchange, the walkthrough covers sign-up, verification and these settings in order.
What to check again in three months
Security settings are not a task you complete. They drift, mostly because of things you do yourself: a new phone, a tool you tried once, a device you signed in on at a relative's house and forgot. Four items are worth revisiting, and together they take about five minutes.
The device and session list. Revoke everything you are not actively using. Signing back in is cheap and the list is usually longer than people expect.
The API key list. If it was empty and is no longer empty, that is a finding rather than a housekeeping item. If you created keys for a tool you have stopped using, delete them — a key outlives your interest in the service it was made for.
The withdrawal address list. Read the labels. An address you cannot account for is the single most serious thing you can find on a routine check, because it is what an intruder plants when a waiting period stops them withdrawing immediately.
Which verification methods are accepted. This one changes without you touching it, because platforms add and retire methods. An account that gained a text-message fallback during a redesign is back to the strength of a text message, and nothing would have told you.
Set a recurring reminder if you are the sort of person for whom that works. If you are not, attach the check to something you already do at a predictable interval — the month you renew something, or the week you do your tax records. The point is that it happens without depending on you feeling motivated about security on a particular Tuesday.
What account security settings cannot protect you from
Two honest limits, because a list of settings can give the impression of covering more ground than it does.
None of this protects against persuasion. Every control above governs what somebody else can do without your involvement. If you are the one typing the code, adding the address and authorising the withdrawal because a convincing person on the phone talked you through it, the settings have all functioned correctly and the money is still gone. That is a different defence, built out of habits rather than switches. The guides on scam emails, fake support calls and SIM swaps are about building them.
And none of it protects against the platform itself. A balance held by an exchange is a claim on a company. It can be restricted, the company can have a bad year, and the account's security settings have nothing to say about either. The answer is not to distrust exchanges — they are the right tool for a lot of what people do — but to notice that "how much do I keep here" is a separate question from "how well is this account configured", and that answering the second one very carefully does not answer the first.
None of this makes an account unbreakable, and anyone selling you that word is selling something. What it does is remove the cheap attacks — the ones that work at scale, on people who have not done any of this — and buy you time on the expensive ones. That is the whole job.
Questions that come up
Is it too late to do this if I already have a balance?
No, but the order changes. With a balance already sitting there, do the second factor and the withdrawal whitelist first, and accept that the waiting period will hold withdrawals to each address you add for the period you chose, and that later changes to the list may suspend withdrawals for a while.
Do I need a hardware security key for a small balance?
Probably not as a first step. An authenticator app or a passkey removes the large majority of remote attacks. A hardware key is worth it when the balance is large enough that losing it would change your year.
How long does the whole set-up take?
Around twenty-five minutes if the authenticator app is already installed and you have somewhere to write down backup codes. The part people underestimate is deciding where the backup codes live.
Written from two Binance support pages read in September 2026 — the anti-phishing code page and the withdrawal settings page, both re-read on 3 October 2026 — plus the account's own settings screens. Features and wording change; treat the numbers above as what those pages said on that date, not as a permanent specification. Everything above was read off published documentation rather than tested inside a funded account.